Cross-Pollination from Cyber-Informed Engineering
Cyber-Informed Engineering is coming to secure OT. Can it secure IT as well?
Abstract of Cyber-Informed Engineering: An approach using design decisions and engineering controls to eliminate or mitigate avenues for cyber-enabled attack of OT systems.
On September 28, Benjamin Lampe of Idaho National Laboratory visited LSU to give a presentation on Cyber-Informed Engineering (CIE), a new approach in the control systems discipline. The presentation, plus my discussions with Ben, have led me to think more about how the information security and cybersecurity worlds can be improved by borrowing techniques from electrical engineering and industrial control systems (ICS).
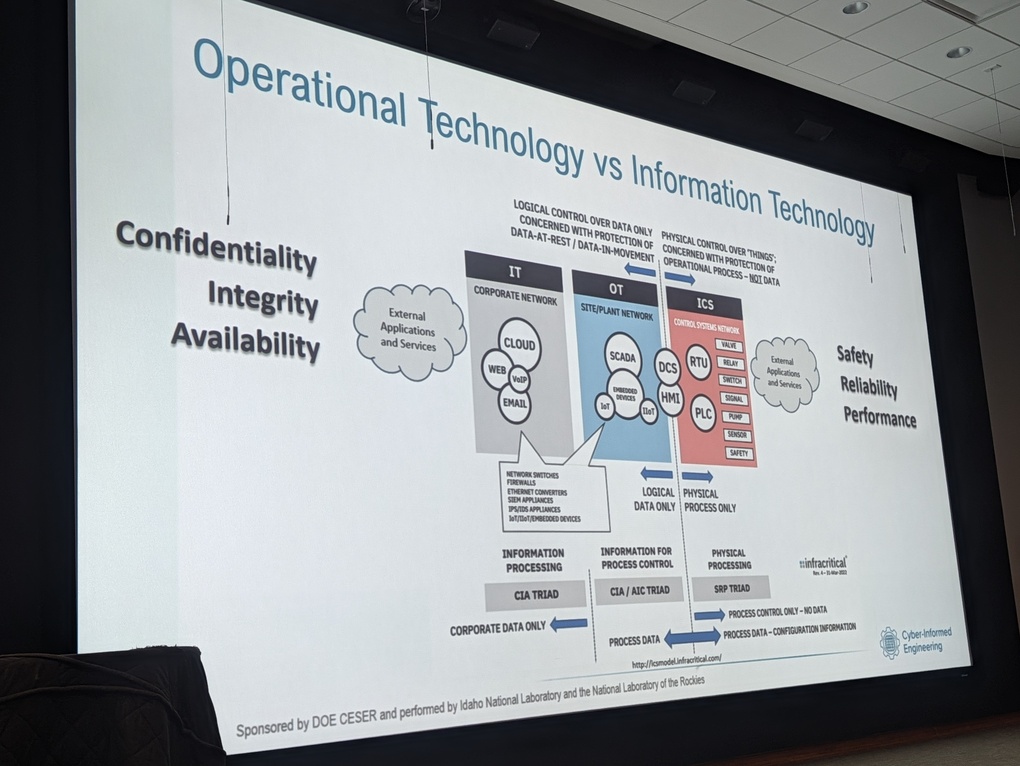
I have no knowledge of ICS at all, much less ICS security. But I have a keen interest in borrowing security approaches from a wide range of fields. So I eagerly attended the talk to learn more. Even simple concepts, incompletely understood, can be helpful when put into different contexts.
As I mentioned a couple of weeks back in LLMs Committing Cybercrimes, Again, and Traffic Lights, it is possible to put guardrails onto non-deterministic systems using relatively simple deterministic systems that look for deviations from normal. It turns out, this is a common implementation in ICS and OT. I took the idea from traffic control systems, but given some of the examples Ben provided, this is a regular approach used in everything from pump stations to electrical substations.
Some of his engineering ideas can still be applied in the InfoSec and IT space, such as one-way enforcement and irreversible actions. This could be implemented via good least privilege (e.g., only allowing a highly vulnerable system to write but not read) or some type of mediating system that writes transactions to a WORM drive.
In all, it was a mind-expanding talk and I am glad I got a chance to attend and ask questions!